
Support for cloud-based Key Management Service
The existing InfoScale support for volume encryption employs Key Management Interoperability Protocol (KMIP)-based Key Management Service (KMS) servers. It works with InfoScale deployments on-premises as well as on the supported cloud platforms.
In addition, InfoScale now supports volume encryption using cloud-based (non-KMIP-compliant, Software as a Service--SaaS) KMSs. Cloud KMS-based encryption is suitable for environments that support high availability and automated configurations. With this release, InfoScale supports AWS and Azure as cloud KMS providers for volume encryption.
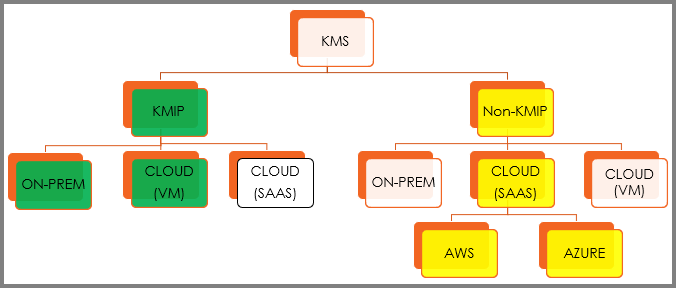
With a cloud-based KMS, you can:
-
Avoid managing complex passphrases manually.
-
Assign a unique master key to each disk group.
-
Recover the master key - within a defined waiting period - after a disk group is removed from the system.
-
Use a single cloud KMS key to encrypt or retrieve the volume encryption key for all volumes within a disk group.
-
Enable access control and auditing for KMS operations to enhance security and compliance.
For details, refer to the following documents:
-
InfoScale 9.1 Installation and Upgrade Guide
-
InfoScale 9.1 Storage Foundation Administrator's Guide
Related information